$ whoami
 security researcher · australia
WahidFayad.
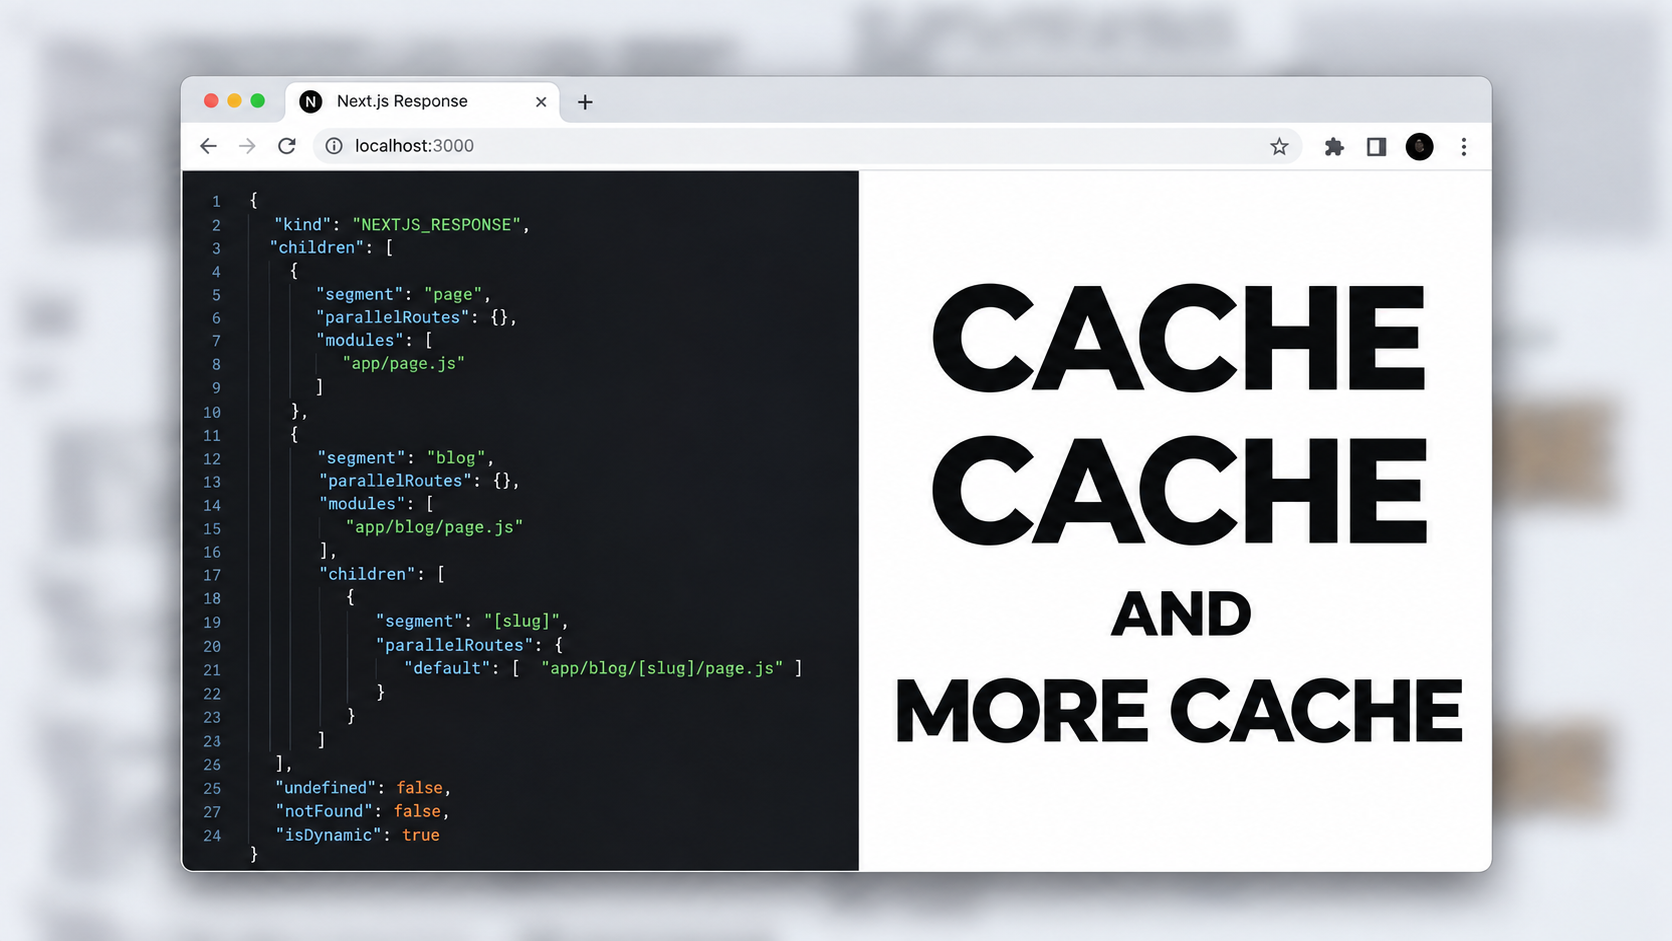
I look for vulnerabilities in web apps, APIs and enterprise systems, then report them. Focused on HTTP behaviour, middleware handling, cache poisoning and supply chain attack surfaces.
trace: request → edge → origin● live
Top 3Australia, HackerOne national leaderboard 2025
100k+global domains affected, valid Google report
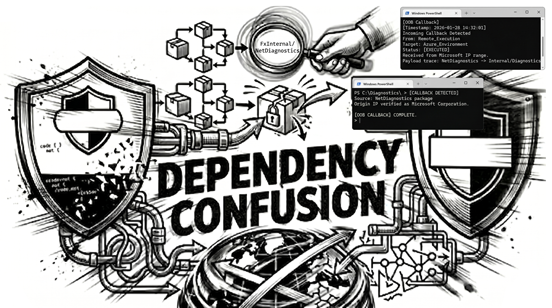
9.3critical dependency confusion finding, written up
// whoami
Protocol-level, not surface-level.
I’m an independent security researcher based in Australia, specialising in high-impact web application vulnerabilities and supply chain attack surfaces. My work focuses on identifying systemic weaknesses in enterprise environments before they can be exploited.
In 2025, I ranked Top 3 in Australia on the HackerOne national leaderboard. I actively contribute to responsible disclosure programs across global platforms: payment processors, SaaS providers and large-scale cloud infrastructure.
My research emphasises HTTP behaviour analysis, middleware handling, dependency confusion, cache poisoning and modern web attack chains. I approach security through deep protocol-level understanding rather than surface testing.
// hacking progress & disclosures
Timeline.
2026
● active
Ongoing research & disclosures
- Actively researching and submitting disclosures across multiple programs
2025
milestones
Finished Top 3 in Australia, HackerOne national leaderboard ↗Valid Google report, vulnerability affecting 100,000+ global domains
- Social media platforms
- Global payment processors
- Enterprise SaaS providers
- Search & recruitment portals
- Additional programs under review
2024
disclosures
Responsible disclosures submitted
- Finance platforms
- eCommerce and payment service providers
- Government technology infrastructure
- Consumer electronics brands
- Job listing services
Dupes
valid, duplicate
Duplicate valid findings
- Multiple tech and cloud service providers
- Bug bounty platforms
- Education and developer tools vendors
- Government and public-sector web services
- Global eCommerce companies
// credentials
Certs & background.
2024coursera ↗Google Pro Cyber Security Analyst2024pdf ↗PentesterLab Unix Badge2024pdf ↗PentesterLab Essential Badge2024pdf ↗PentesterLab Recon Badge
educationCertificate IV, Information Technology (Web Design)
experience
- Security researcher: web app & enterprise vulnerabilities
- Bug bounty hunter: responsible disclosure across multiple programs
- CTF participant: active since November 2023
// blog
Write-ups.
Let’s talk.
Have a collaboration opportunity, disclosure inquiry, or just want to connect? Reach out on any of these platforms.